
PHP2Shell emergency response
WordPress
WooCommerce
Magento
Laravel
Drupal
Custom PHP
Legacy PHP
PHP2Shell: critical PHP vulnerabilities? Get expert help before your business is disrupted.
Mars Innovation Technology helps organizations identify exposed PHP environments, implement appropriate emergency safeguards, and patch business-critical applications safely.
Free initial consultation. Engineering engagements from CAD $2,500. Scope confirmed before invoicing.
- Understand your exposure
- Stabilize critical services
- Patch and verify safely
Request a free consultation
Request a free 15-minute call. Leave passwords, keys, and connection details out of this form. Nothing is charged here, and this form does not pick a time on a calendar. We reply by email or phone to set the 15 minutes.
Delivered with Seya Group
Security and DevSecOps scope inside this fixed-price package is delivered with Seya Group. For security and DevSecOps consulting, see their team directly.
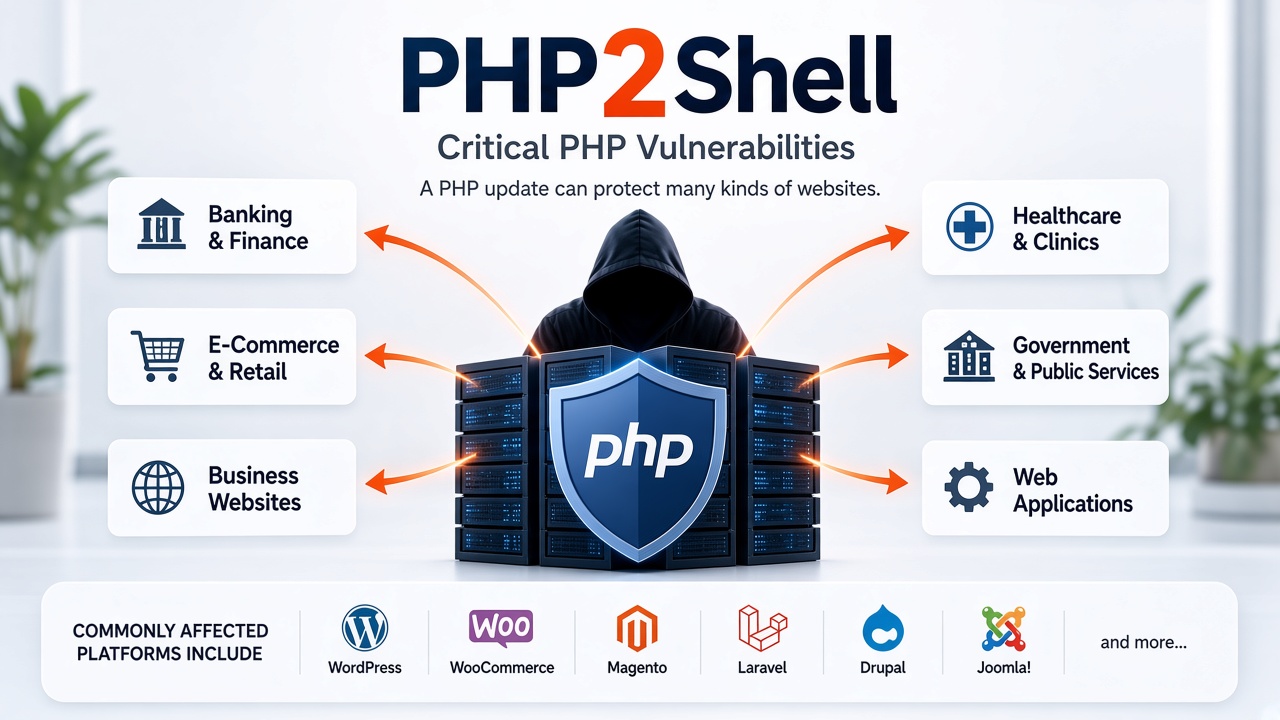
A PHP issue can affect banks, government sites, stores, clinics, and other websites.
Verified advisory
What was confirmed on 21 October 2026
Security advisory information last verified: 22 October 2026
The PHP project reported that PHP 8.5.12, 8.4.27, 8.3.36, and 8.2.35 fix two critical vulnerabilities that can allow unauthenticated remote code execution on PHP installations serving web requests. The PHP project’s 20 October 2026 advance notice rated both issues CVSS v4.0 9.2.
CVE-2026-109618 is described as remote code execution via out-of-memory corruption. CVE-2026-109619 is described as remote code execution via stale global state. The PHP project says risk is highest for mod_php, where a demonstrated exploit can run before application code. CISA’s 21 October 2026 alert had not observed exploitation as of that publication, and later reporting describes exploitation attempts. This page does not describe exploit steps.
Not every PHP website is vulnerable. A site already on those fixed releases, or on a vendor build that includes the fixes, is not described as still affected by these two issues. PHP 8.1 and older no longer receive updates from the PHP project. Some vendors backport fixes. PHP 8.2 reaches end of life on 31 December 2026.
There is no complete mitigation short of an update. The PHP project says temporary configuration changes reduce specific attack paths and do not make an installation safe. CISA notes a web application firewall may provide some protection until systems are patched. A WAF is not a complete patch, and it does not guarantee protection. Some environments may need isolation until patched.
How we work
Response
Emergency response available
Start time is confirmed after your consultation and a written scope. We do not guarantee same-day deployment.
Uptime
Business continuity focused
Emergency controls are planned to keep the application available where that is possible.
PHP
Legacy PHP expertise
PHP 7 and 8 applications, including WordPress, WooCommerce, Magento, Laravel, and custom code.
Scope
Written engagement scope
Sales confirms scope and pricing before any invoice. Published starting points begin at CAD $2,500.
Who this is for
Outdated PHP can expose a business. The framework name alone does not prove it.
Running WordPress, WooCommerce, Magento, Laravel, or a custom PHP application? Those products run on PHP. An outdated or unpatched PHP environment may expose the business to serious security vulnerabilities.
On 21 October 2026 the PHP project shipped emergency releases for two critical remote-code-execution issues, CVE-2026-109618 and CVE-2026-109619. Our engineers help you stabilize exposed services, apply appropriate safeguards, and patch business-critical applications safely.
You are not sure which PHP version production is actually running.
A security advisory, host notice, or insurer asked you to patch.
The site has to stay up while the runtime is updated.
Plugins, themes, or custom code may not run on a newer PHP version.
A web application firewall is in place, and you have been told that is enough. It is not a patch.
Two-stage PHP security response
Reduce exposure first. Then patch for good.
Emergency controls reduce risk but do not replace security patches.
Stage 1
Emergency protection
Reduce immediate security exposure while keeping the application operational wherever possible.
- Initial security assessment
- PHP version and configuration review
- Exposure assessment
- Cloudflare WAF configuration where it applies
- NGINX or ModSecurity where it applies
- Access restrictions
- Request filtering
- Rate limiting
- Security monitoring
- Initial remediation recommendations
Stage 2
Permanent remediation
Apply the runtime fix, prove the application still works, and leave you with a verified production deploy.
- PHP runtime patching
- Legacy PHP migration
- Code compatibility updates
- Dependency upgrades
- WordPress and WooCommerce compatibility
- Magento compatibility
- Laravel compatibility
- Custom PHP application updates
- Security testing
- Production deployment
- Post-remediation verification
Workflow
From the live site to a longer-term fix
The picture is illustrative. The sequence below is the engagement path.
Customer website
Emergency assessment
WAF / security controls
Risk reduction
PHP patching
Application compatibility
Security validation
Long-term protection
What we deliver
A path from emergency protection to verified patching
Each later stage is optional and scoped in writing. Published starting points begin at CAD $2,500.
Emergency protection
Assessment, exposure review, and interim controls for one production site. Controls are not a substitute for the PHP patch.
Permanent remediation
Patch or migrate the runtime, test application compatibility, deploy, and verify. Scoped after the initial assessment.
Multi-system coordination
When more than one PHP application must be stabilized and patched with shared verification and reporting.
Managed follow-through
After remediation, ongoing monitoring and maintenance can be proposed. It is scoped separately from rapid triage.
Platform review scope
PHP Platforms and Applications Worth Reviewing
These products can run on PHP. Inclusion is not a finding that the product is vulnerable, and it is not a vendor endorsement. Exposure depends on the PHP version actually serving requests.
All
CMS
Commerce
Publishing
Learning
Collaboration
Framework
Database admin
Analytics
Hosting billing
Webmail
Community
ERP
Data and commerce
Marketing
Wiki
CRM
Hosting panel

WooCommerce

Magento Open Source

Drupal

Joomla

PrestaShop

Shopware 5
Shopware 6
October 2026 PHP vulnerabilities
How organizations responded
Each card summarizes only what its linked source states, such as precautionary maintenance or a service reported offline. Sources reviewed 22 October 2026.
BambooHR
BambooHR (US, Canada, Ireland)
21 October 2026
Took BambooHR offline as a precaution in response to PHP2SHELL, applied the recommended fix, and reported the service back online the same day.
Source: BambooHR status page
BASE, Inc.
BASE online shop platform, PAY ID app, BASE API
21 October 2026
Brought forward emergency maintenance to 15:50 JST as a precaution after a critical PHP vulnerability; the notice says no unauthorized access or data leak had been confirmed.
Source: BASE help center notice (Japanese)
GMO Pepabo
Color Me Shop (カラーミーショップ)
21 October 2026
Paused shop pages and the admin console from 22:00 JST as a precautionary PHP security measure and reported maintenance complete at 08:49 JST on 22 October.
Source: Color Me Shop notice (Japanese)
kubell
Chatwork
21 October 2026
Ran emergency server maintenance from about 23:00 JST to 00:15 JST as a precaution against a critical PHP vulnerability; the service was unavailable during that window.
Source: Chatwork help center notice (Japanese)
GMW
pictSQUARE
21 October 2026
ITmedia NEWS reported that pictSQUARE entered emergency maintenance and that the action was PHP-related, based on company announcements and its own reporting.
Source: ITmedia NEWS (Japanese)
Cygames
Umamusume, Granblue Fantasy, Shadowverse: Worlds Beyond
21 October 2026
GAME Watch reported simultaneous maintenance across several Cygames titles to address a PHP vulnerability on their servers, with no damage or data leak confirmed at the time.
Source: GAME Watch (Japanese)
asken
asken diet app, web, and corporate admin
22 October 2026
Paused all asken services from about 22:50 JST as a precaution during PHP patching and reported a full restart at 09:25 JST on 22 October.
Source: asken company notice (Japanese)
bizocean
bizocean templates, journal, DX comparison, admin consoles
22 October 2026
Suspended all bizocean sites from the evening of 21 October as a precaution after the PHP vulnerability notice and reported service restored at 14:35 JST on 22 October.
Source: bizocean notice (Japanese)
Sony (Japan)
Sony product information and Sony Store sites
21 October 2026
Posted an emergency maintenance notice for PHP vulnerability response starting the night of 21 October, warning that the website and some services may be unavailable.
Source: Sony Japan maintenance notice (Japanese)
Japan Airlines
Parts of the JAL website
22 October 2026
Temporarily closed certain website pages and services as a preventive measure over a PHP vulnerability, stating there was no impact on bookings, ticketing, or flight operations.
Source: JAL website notice
Bushiroad
Group websites and systems
21 October 2026
Denfaminicogamer reported Bushiroad group websites still in maintenance on 22 October and quoted a Bushiroad post announcing emergency maintenance over a PHP vulnerability.
Source: Denfaminicogamer (Japanese)
Hokkaido Shimbun
Hokkaido Shimbun Digital and corporate site
22 October 2026
Paused PHP-based features and ran emergency maintenance on its corporate site from about 13:00 JST, stating this was not due to unauthorized access or a data leak.
Source: Hokkaido Shimbun notice (Japanese)
Kyushu Electric Power
Corporate website
22 October 2026
Saga TV, reporting on PHP-related outages in Saga Prefecture, said Kyushu Electric Power had been running similar maintenance since the night of 21 October and its website was reported offline.
Source: Saga TV (Japanese)
LIFULL
LIFULL HOME'S and related sites
21 October 2026
Placed LIFULL HOME'S, its corporate site, and several related services into emergency maintenance from 20:00 JST after a critical PHP vulnerability, with no end time announced.
Source: LIFULL maintenance notice (Japanese)
CoDMON
CoDMON childcare platform and parent app
22 October 2026
Suspended all services as a precaution after a critical PHP vulnerability was disclosed and resumed most of them at 03:22 JST on 22 October after patching.
Source: CoDMON press room notice (Japanese)
pixiv
pixiv, pixivFANBOX, BOOTH, and related services
21 October 2026
Nikkei xTECH listed pixiv among services that announced emergency maintenance in response to the PHP vulnerabilities.
Source: Nikkei xTECH (Japanese)
Dwango
Niconico
21 October 2026
Began precautionary maintenance across several Niconico services from 19:00 JST and later updates describe the work as a response to the PHP vulnerability.
Source: Niconico Info notice (Japanese)
Hanshin Electric Railway
Corporate website
21 October 2026
Kyodo News reported that Hanshin Electric Railway would temporarily suspend its website after the PHP flaw; the company notice cites a software vulnerability and says it was not caused by unauthorized access.
Source: Kyodo News via Yahoo! News Japan (Japanese)
Creema
Creema site and app
21 October 2026
Ran precautionary maintenance from 16:45 JST citing the security situation of external software; the announcement does not name PHP.
Source: Security Measures Lab (Japanese)
Pricing
Engagements in Canadian dollars
Published starting points in CAD. Final scope and pricing are confirmed after the free consultation, before any invoice.
Most Popular
Rapid Triage & Stabilization
CAD $2,500
Up to one scoped engineer-day
Up to one scoped engineer-day. Does not guarantee that every vulnerability is fixed in one day.
- PHP runtime review
- Exposure verification
- Infrastructure assessment
- Risk-ranked findings
- Feasible interim safeguards
- Emergency remediation plan
- Written report
Patch & Verify
From CAD $7,500
Scoped after consultation
Patch the runtime, test compatibility, deploy with rollback planning, and verify the change.
- PHP runtime patching
- Dependency compatibility
- Testing
- Deployment
- Rollback planning
- Post-change verification
- Written completion report
Multi-System Response
From CAD $15,500
Multiple PHP applications
Coordinate emergency work across more than one PHP application with verification and reporting.
- Multiple PHP applications
- Cross-system coordination
- Engineering workstreams
- Emergency response
- Controlled patching
- Verification and reporting
Custom Enterprise Response
Quoted individually
Proposal after consultation
A CAD $2,500 paid discovery may be proposed after the free consultation. Our sales team decides when to invoice and whether that fee is credited. Not charged on this website.
- Discovery after the free consultation
- A written proposal and statement of work
- Invoice issued by the sales team only after acceptance
Compare
A patch is the fix. Controls only reduce exposure.
Choose the column that matches what you need this week.
| Feature | Mars engagement | WAF only | Wait |
|---|---|---|---|
Confirms the PHP version in production | ✓ | ✗ | ✗ |
Interim controls while a patch is planned | ✓ | Partial | ✗ |
Replaces the need to patch | ✗ | ✗ | ✗ |
Application compatibility testing on a remediation engagement | ✓ | ✗ | On you |
Written scope before invoicing | ✓ | ✗ | ✗ |
Cyber insurance support
Documentation your insurer can review
If your business has experienced a security incident, some response and recovery expenses may be eligible under your cyber insurance policy.
Our team can assist with technical documentation, incident response coordination, and remediation planning.
Coverage depends on your policy and insurer approval. We do not promise reimbursement. Preventive upgrades are not automatically covered.
Request insurance-related assistanceQualification
Is this a fit?
We take production PHP applications that need an engineer, not a scanner report.
Likely a fit
A production PHP site you need to keep online.
WordPress, WooCommerce, Magento, Laravel, Drupal, Joomla, or custom PHP.
You can name the hosting provider, even if the PHP version is unknown.
You can approve a scoped engagement after the free consultation.
You will share access later through a secure process, not in this form.
Likely not a fit
A request to scan or exploit a site you do not own.
A guarantee that a WAF alone makes the site safe.
Expecting a fixed-price invoice before sales confirms scope.
Sending us passwords, SSH keys, or database credentials by email or form.
An assumption that every PHP site is vulnerable regardless of version.
Why Mars Innovation Technology
Engineers, a written scope, and a consultation-first path
Legacy PHP and cloud work
The same studio that ships application, cloud, and infrastructure engagements takes the PHP runtime and the surrounding hosting into account.
Security engineering, not a slogan
Assess exposure, reduce it, patch, test compatibility, then verify. We will tell you what is still open.
Business continuity
Emergency work is planned around keeping the site available where the hosting and the code allow it.
Transparent scope
Published starting points begin at CAD $2,500. Broader work is confirmed in writing before any invoice.
No online charge on this site
The consultation is free. Engagements are invoiced by the sales team only after you accept scope. This website does not collect card numbers.
A clear sequence
Consult, confirm scope, assess, deploy emergency controls, then execute agreed remediation. You see each stage in writing.
Engagement
What happens after you request a consultation
This is not an online sale and not an invoice. Sales confirms scope before any invoice. Scheduling a meeting does not reserve a calendar slot unless a calendar provider confirms it.
1
Free consultation
You book a 15-minute consultation or submit the form. We use your details only to follow up — not to charge you on this website.
2
Scope confirmation
After the meeting, sales confirms whether an engagement is appropriate, which package fits, and what access is needed. No invoice until you accept written scope.
3
Assessment and controls
An engineer reviews the environment and deploys the emergency controls that fit it.
4
Remediation and verification
If a patch or migration is still required, we execute the agreed workstream and verify the result.
Questions
Straight answers
Sources for the advisory answers are linked in the verified advisory section.
Is my PHP website vulnerable?
Not automatically. The 21 October 2026 PHP advisory applies to installations serving web requests that are not yet on PHP 8.5.12, 8.4.27, 8.3.36, or 8.2.35, or an equivalent vendor backport. PHP 8.1 and older are outside PHP project support. WordPress, WooCommerce, Magento, Laravel, Drupal, Joomla, and custom PHP can all run on PHP, but the product name does not prove exposure. We confirm version, exposure, and hosting during an assessment. This page does not scan your site.
Can you protect my website without downtime?
Emergency protection is planned to reduce exposure while keeping the application available where that is possible. A PHP upgrade can still need a maintenance window. We confirm that during assessment. We do not promise zero downtime.
Is a WAF enough to stop PHP attacks?
No. CISA says a web application firewall may provide some protection until systems are patched. The PHP project says there are no complete mitigations and updating is the only safe choice. Emergency controls reduce risk. They do not replace patches, and a WAF is not a complete patch.
Do I need to upgrade PHP?
If production is below the fixed releases and you do not have a vendor backport, the PHP project and CISA recommend updating. PHP 8.1 and older no longer receive updates from the PHP project. PHP 8.2 reaches end of life on 31 December 2026.
Can you fix PHP 7 applications?
We can assess PHP 7 applications and plan a migration or a vendor-supported path. The PHP project published minimal source backports for 7.4, 8.0, and 8.1 for people building from source. Patch & Verify starts from CAD $7,500 and is scoped after the consultation.
Will upgrading PHP break WooCommerce?
It can, if plugins, themes, or custom code are incompatible with the new runtime. Remediation engagements include compatibility testing before production deployment. We do not promise a specific plugin will keep working without testing it.
How quickly can emergency protection begin?
After the consultation and once scope is confirmed in writing, scheduling depends on engineering capacity and the urgency you report. We do not guarantee same-day deployment.
Can you work with my hosting provider?
Yes. Shared, cloud, dedicated, and managed hosting can all be assessed. Access is arranged after kickoff through a secure credential process. Do not send passwords, SSH keys, database credentials, or API keys in this form.
Can cyber insurance cover remediation?
Some incident response and recovery expenses may be eligible under your policy. Coverage depends on the policy and the insurer’s approval. We can help with technical documentation, coordination, and a remediation plan. We do not promise reimbursement, and preventive upgrades are not automatically covered.
How much does emergency PHP remediation cost?
Rapid Triage & Stabilization is CAD $2,500 for a scoped engineer-day. Patch & Verify is from CAD $7,500, Multi-System Response from CAD $15,500, and Custom Enterprise Response is quoted individually. Final scope and pricing are confirmed after the free consultation, before any invoice.
Mars Innovation Technology, Burnaby, BC. Free consultation — not a reserved slot unless a calendar provider confirms it. This request is not a sale and not an invoice. Sales confirms scope before any invoice. We use your details only to follow up on this PHP security request.